AI Fraud Risks for Fintechs in India: A Response Plan
AI fraud risks for fintechs in India require stronger API controls, rapid incident triage, clear customer communications and carefully designed protection journeys.
Article brief
9 November 2026
11 min read
By Bharatsure Team
Category
Insurance infrastructure
Share
LinkedInQuick answer
A response plan for Indian banks, NBFCs, fintechs and payment platforms facing AI-assisted attacks on payment APIs, onboarding and customer-support journeys.
- CERT-In’s public advisories dated 9 October and 4 November 2026 describe AI-assisted attacks that can compromise payment and disbursement APIs, bypass application controls and move funds through mule accounts.
- The advisory’s technical controls are recommended actions. Separate CERT-In Directions require covered entities to report listed cyber incidents within six hours of noticing them and retain ICT logs for a rolling 180 days.
- Prevention remains the first line of defence. Embedded cyber or UPI-fraud protection can complement it only when the policy wording, customer communication, evidence capture and claims hand-off are designed together.
AI fraud risks for fintechs in India are no longer limited to suspicious messages or isolated account-takeover attempts. Product, risk and partnership teams need to assume that attackers can automate reconnaissance, tailor exploits quickly and test payment flows at scale. The response is to secure the transaction path end to end, triage suspected incidents fast, communicate clearly with customers and use insurance only as a carefully scoped complement to prevention.
What the reported AI-fraud warning means for fintechs in India
CERT-In issued Advisory CIAD-2026-0046 on 9 October 2026 and followed it with Advisory CIAD-2026-0058 on 4 November 2026. The update describes an AI-assisted campaign against NBFCs, digital lending platforms, fintechs, payment aggregators, payment service providers and other BFSI entities. It says attackers can survey targets at machine speed and abuse payment or disbursement APIs. CERT-In’s 4 November 2026 advisory sets out the campaign and its recommended actions.
The earlier advisory describes a practical failure mode: an attacker who compromises an internet-facing application, a privileged endpoint or credentials may invoke fund-transfer APIs from whitelisted infrastructure. This can bypass checks expected earlier in the application journey, including KYC, sanction, beneficiary verification and balance checks. It also records dummy transaction references, transfers to mule accounts, rapid high-value movements and attempts to delete or truncate logs. CERT-In’s 9 October 2026 advisory sets out these patterns and recommended defensive actions.
This matters because AI powered fraud in Indian banking can compress the time between a technical compromise and a financial loss. A control designed only for a manual attacker may not withstand continuous, automated attempts that probe limits and adapt to system responses.
The advisory’s control list is recommended guidance, not a new standalone rule. Under the CERT-In Directions of 28 April 2022, service providers, intermediaries, data centres, body corporates and government organisations must report listed cyber incidents within six hours of noticing them or being informed of them, and must retain ICT-system logs for a rolling 180 days. Separately, the Reserve Bank of India (Small Finance Banks - Cybersecurity, Technology: Risk, Resilience and Assurance Framework) Directions, 2026 require small finance banks to report cyber incidents on the DAKSH platform within six hours of detection. Each fintech should map its own obligations with counsel, its regulated partner and its incident-response provider.
AI fraud risks for fintechs in India: the response in brief
Build the response around four workstreams:
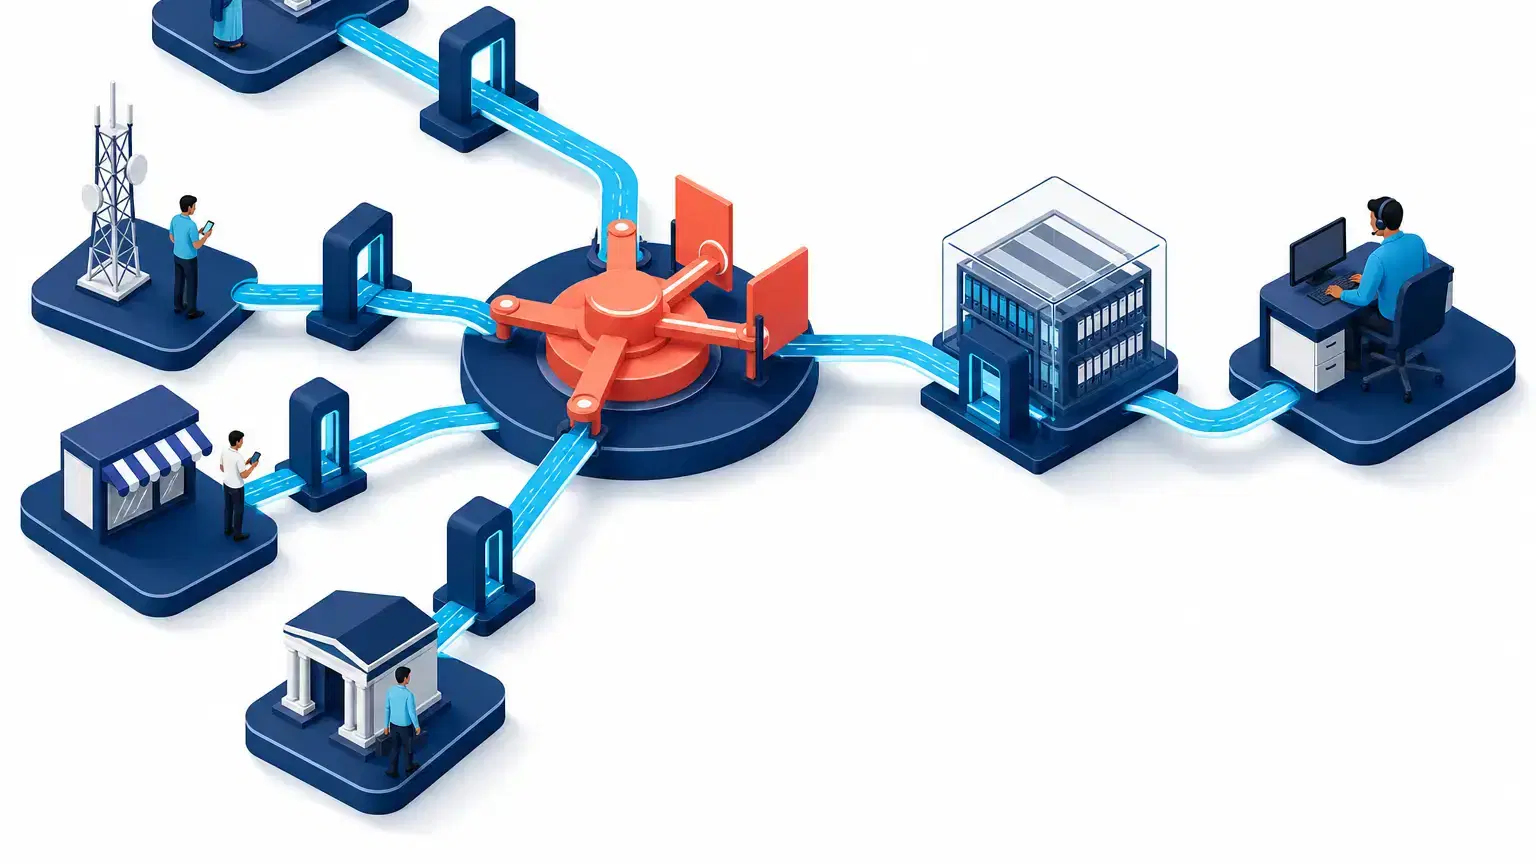
- Protect the money-moving path. Treat every disbursal, payout, settlement and reversal API as a high-risk control plane. Validate state transitions on the server, not merely in the client app.
- Detect and contain at speed. Combine real-time payment monitoring with authority to hold, step up or stop suspicious flows. Ensure the security, fraud and payments teams can act without a long hand-off chain.
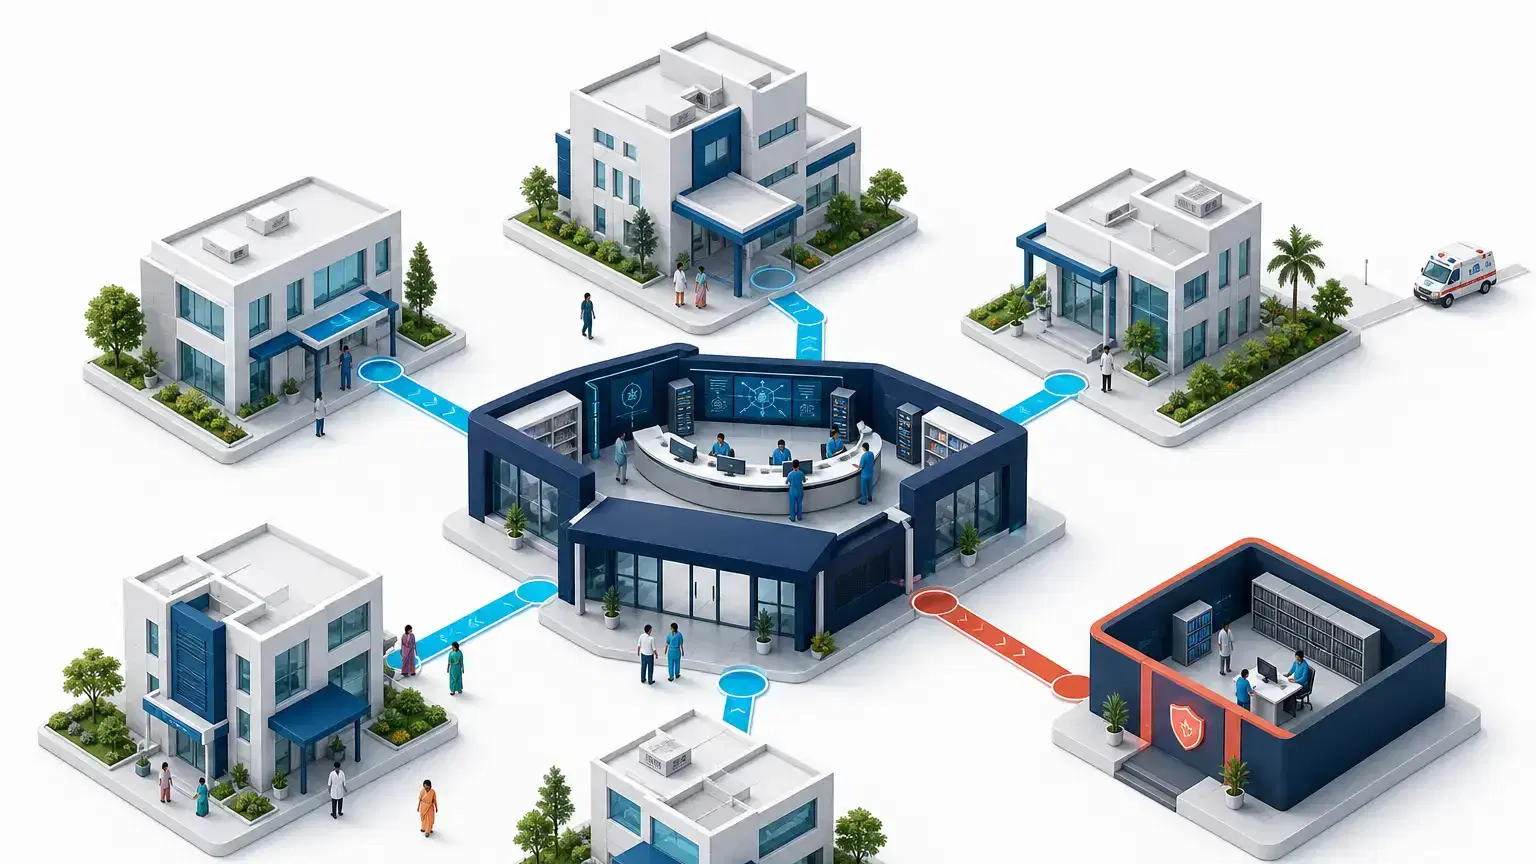
- Preserve evidence and meet reporting duties. Keep immutable logs, reconcile continuously and prepare a six-hour reporting playbook for events that fall within the CERT-In Directions.
- Support customers without overpromising. Give immediate safety steps, payment-dispute routing and a structured fraud report. If protection cover is offered, describe eligibility and claims assessment exactly as the policy allows.
This is fintech fraud risk management in India as an operating-design problem, not only a model-selection exercise. The product interface, identity checks, API architecture, treasury operations, support scripts and partner contracts must reinforce one another.
Where AI-enabled impersonation can disrupt onboarding, payments and support
Onboarding and account recovery
Synthetic identity fraud in India can involve fabricated profiles, manipulated identity evidence or deepfake-assisted attempts to defeat video, facial or liveness checks. Treat onboarding as one signal in a wider decision, not a single pass-or-fail event. Compare device, behavioural, document, account and transaction signals, then require additional review where the signals do not align.
Account recovery deserves the same care as onboarding. A convincing voice or video call should not independently reset credentials, replace a registered device or raise transaction limits. Use out-of-band confirmation, cooldown periods for material profile changes and rules that distinguish a familiar device from a newly enrolled one.
Payments, payouts and merchant settlement
CERT-In advises server-side transaction validation, maker-checker approvals, reconciliation, amount and velocity controls, new-beneficiary checks, secure secret management and API request signing. Its updated advisory also flags a pattern in which micro-value tests can precede a larger unauthorised transfer. The 4 November 2026 advisory recommends holding or reviewing this pattern alongside cooling periods and anomaly detection.
For lending platforms, bind each disbursal to a valid sanctioned record and cryptographically bind the stages of the transaction. For payment aggregators, apply the same discipline to merchant-settlement instructions. Do not treat an API call as legitimate merely because it arrives from a recognised network location or a signed client app.
Customer support and social engineering
Deepfake fraud prevention for banks and fintechs should extend beyond biometric checks. A fraudster may impersonate support staff, a family member, a senior executive or a public official to create urgency. RBI has identified deepfake-driven impersonation, bogus call centres and mule-account networks as tactics used in authorised push-payment fraud, where a customer is manipulated into approving the payment. RBI’s discussion paper on digital-payment fraud safeguards explains why post-transaction recovery can be difficult.
Make official support channels easy to verify. Give customers plain warnings that staff will not ask for a UPI PIN, OTP, remote-device access or a payment to “secure” an account. Train agents to recognise panic, coercion and unusual recovery requests, then move the customer to a controlled verification route.
A fraud-control checklist for product and risk teams
Use this checklist to turn the advisory into an owned programme:
- Inventory every API that can create, approve, release, settle, reverse or modify a financial transaction. Retire unused and unauthenticated endpoints.
- Remove long-lived secrets from code and configuration. Store credentials in an approved secrets-management system, rotate them and use short-lived, least-privilege access tokens.
- Separate environments. UAT, staging and production should not share credentials, tokens, databases or direct network paths. Apply production-grade monitoring to internet-facing non-production systems.
- Make every payment rule server-side. Validate the transaction’s sequence, approved reference, beneficiary, amount, limits and sufficient balance before a payout API can execute.
- Use layered transaction controls. Apply maker-checker approval, beneficiary verification, per-transaction and cumulative limits, velocity rules, amount-band anomalies and new-beneficiary cooling periods.
- Monitor continuously. Centralise cloud, endpoint and API logs; protect them from tampering; reconcile internal records with bank, gateway and aggregator statements in near real time.
- Plan containment. Pre-authorise emergency actions such as disabling compromised accounts, suspending specific APIs, rotating credentials and placing controlled holds on suspicious transaction routes.
- Test the response. Run scenario exercises across fraud, information security, operations, legal, customer support and partner-bank teams, including weekends and holidays.
CERT-In recommends 24x7 monitoring, increased staffing and lower alert thresholds during low-coverage periods, followed by forensic verification after an incident because incomplete remediation can lead to repeat compromise. Its 4 November 2026 update provides technical detail that security teams can convert into environment-specific controls.
When embedded cyber or UPI-fraud cover can complement prevention
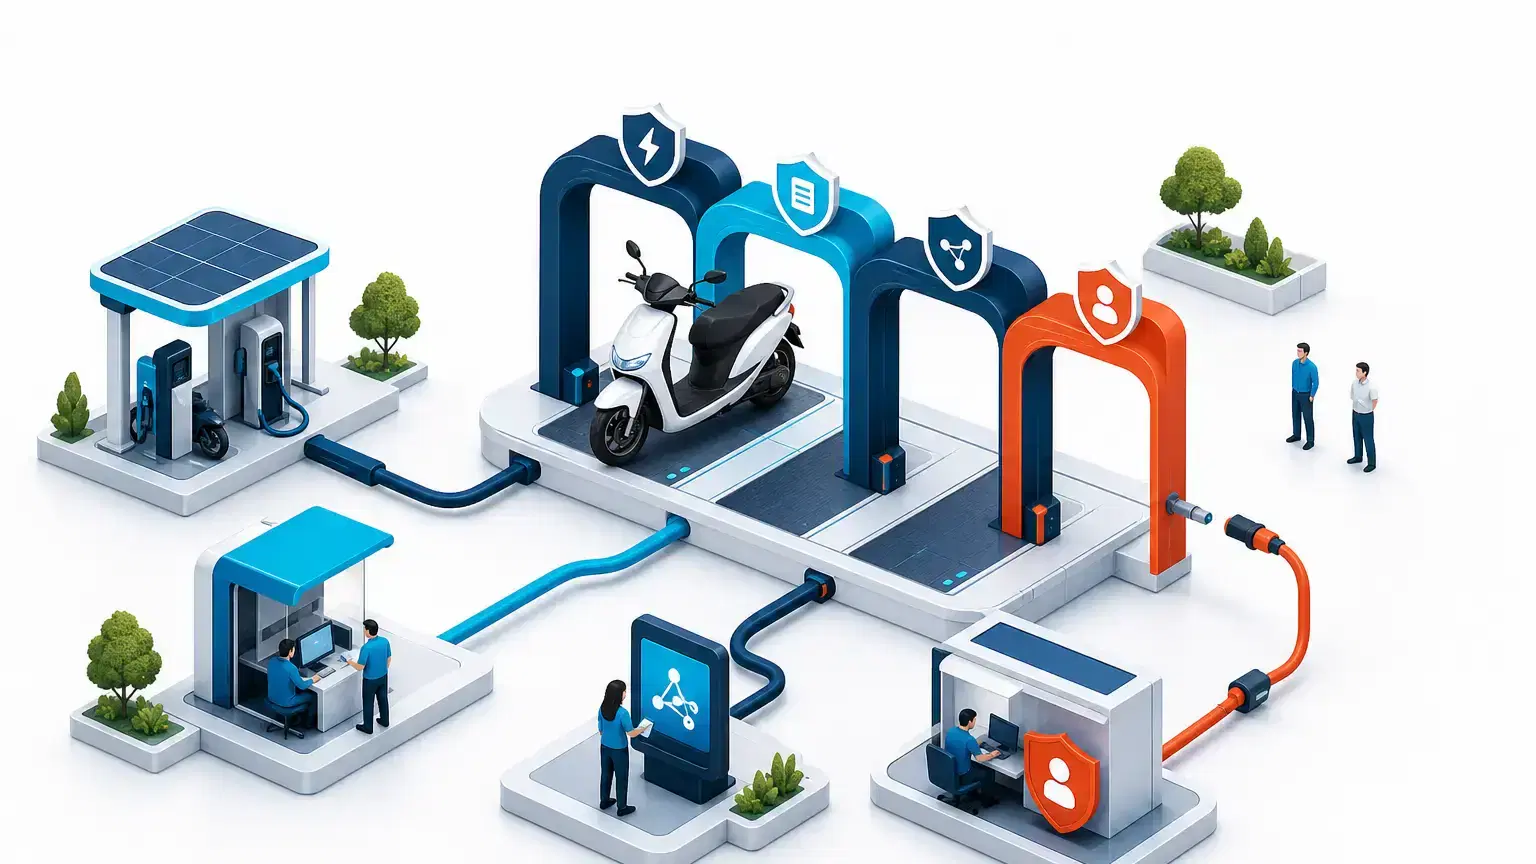
Insurance is not a substitute for strong authentication, secure APIs, monitoring or complaint handling. It can form part of an embedded protection proposition when it addresses a defined residual loss and is presented at a relevant customer moment, such as account activation, a security-centre interaction, UPI setup or a paid-plan renewal.
A fintech considering embedded cyber cover should first agree the covered event with the insurer. A customer-authorised payment after deception may be eligible only if the policy expressly covers that social-engineering scenario. It is not automatically covered simply because funds moved through UPI. UPI fraud cover design explains why the policy definition, exclusions, evidence, limits and reporting conditions need to be tested together.
The partner journey should state that cover is subject to policy terms, conditions, exclusions and the insurer’s claims assessment. Do not offer retrospective cover after a suspected scam. At that point, prioritise account safety, payment-dispute routing and claim intimation for customers who already hold eligible cover.
For partners building the programme, AffinityOS insurance infrastructure can support a white-label distribution flow that connects enrolment, servicing and insurer-facing operations.
How to design customer communication and claims intake after a suspected scam
The first customer screen should give actions, not assurances about recovery or claim payment:
- Ask the customer to secure their account and report the transaction to the relevant bank, UPI app or payment provider immediately.
- Show a structured report form that captures transaction ID or UTR, amount, date and time, app or bank involved, fraud channel, relevant screenshots and the customer’s short chronology.
- Route the customer to the National Cybercrime Reporting Portal and the financial-fraud helpline where appropriate. The portal’s complainant checklist asks financial-fraud complainants to keep the bank, wallet or merchant name, 12-digit transaction ID or UTR, transaction date, fraud amount and relevant evidence ready. The portal also lists the cybercrime helpline as 1930.
- Never ask for UPI PINs, OTPs, full card details or other secrets in the support or claims flow.
- Create separate references for the platform case, payment complaint and insurance claim. This reduces confusion when different parties own different decisions.
A good triage workflow preserves evidence without making the customer prove claim eligibility at the first interaction. If cover is available, the claims hand-off should pass only the information needed for assessment, use clear consent and explain that the insurer decides admissibility under the policy terms. A white-label claims infrastructure layer can organise claim intimation, document collection and status communication while keeping those decision boundaries clear.
The closing message should be calm and specific: what the customer should do now, what the platform is doing, what information is needed and when the customer can expect the next update. That is more useful than a generic warning about fraud when the incident is stressful.
FAQs: AI fraud risks for fintechs in India
What are the main AI fraud risks for fintechs in India?
The immediate risks include AI-assisted discovery and exploitation of exposed systems, theft or misuse of credentials, automated API abuse, synthetic or manipulated identity artefacts, deepfake-led social engineering and machine-speed testing of payment flows. CERT-In’s BFSI advisory describes attackers using compromised infrastructure and valid credentials to invoke payment or disbursement APIs directly. CERT-In’s advisory CIAD-2026-0058 provides the public details.
Does the CERT-In advisory create new mandatory controls for every fintech?
No. The 9 October 2026 and 4 November 2026 CERT-In advisories set out recommended defensive actions for the observed campaign. Mandatory reporting and log-retention duties arise separately under the CERT-In Directions of 28 April 2022, where applicable. Regulated entities must also follow their sectoral regulator’s requirements and contractual obligations to partner banks, payment providers and insurers.
Can cyber or UPI-fraud cover pay when a customer authorises a transfer after being deceived?
It can only do so when the issued policy expressly covers the relevant social-engineering or authorised-payment fraud event. A customer-approved transfer is not automatically an insured loss. The policy wording, exclusions, limits, reporting conditions and insurer assessment determine whether a claim is payable. BharatSure’s guide to UPI fraud cover design sets out this distinction for fintech product teams.
What should a fintech collect after a customer reports a suspected scam?
Capture the transaction reference or UTR, amount, date and time, payment-app or bank details, scam channel, available screenshots or messages, complaint references and a short chronology. Do not collect secrets such as UPI PINs, OTPs or full card credentials. The National Cybercrime Reporting Portal’s checklist specifically asks financial-fraud complainants to keep transaction and institution details, the fraud amount and relevant evidence ready. Route the customer to their bank or payment provider and the portal as appropriate, while preserving evidence needed for investigation or an eligible insurance claim.
Book a demo to explore a white-label cyber or fraud-protection journey, with servicing and claims workflows built for your platform.
Frequently asked questions
What are the main AI fraud risks for fintechs in India?
The immediate risks include AI-assisted discovery and exploitation of exposed systems, theft or misuse of credentials, automated API abuse, synthetic or manipulated identity artefacts, deepfake-led social engineering and machine-speed testing of payment flows. CERT-In’s BFSI advisory describes attackers using compromised infrastructure and valid credentials to invoke payment or disbursement APIs directly.
Does the CERT-In advisory create new mandatory controls for every fintech?
No. The 9 October 2026 and 4 November 2026 CERT-In advisories set out recommended defensive actions for the observed campaign. Mandatory reporting and log-retention duties arise separately under the CERT-In Directions of 28 April 2022, where applicable. Regulated entities must also follow the requirements of their sectoral regulator and their contractual obligations to partner banks, payment providers and insurers.
Can cyber or UPI-fraud cover pay when a customer authorises a transfer after being deceived?
It can only do so when the issued policy expressly covers the relevant social-engineering or authorised-payment fraud event. A customer-approved transfer is not automatically an insured loss. The policy wording, exclusions, limits, reporting conditions and insurer assessment determine whether a claim is payable. BharatSure’s UPI fraud cover design guide explains the distinction for fintech product teams.
What should a fintech collect after a customer reports a suspected scam?
Capture the transaction reference or UTR, amount, date and time, payment-app or bank details, scam channel, available screenshots or messages, complaint references and a short chronology. Do not collect secrets such as UPI PINs, OTPs or full card credentials. Route the customer to their bank or payment provider and the National Cybercrime Reporting Portal as appropriate, while preserving evidence needed for investigation or an eligible insurance claim.
Sources
- CERT-In’s 4 November 2026 advisory — cert-in.org.in
- CERT-In’s 9 October 2026 advisory — cert-in.org.in
- CERT-In Directions of 28 April 2022 — cert-in.org.in
- RBI’s Master Direction on Information Technology Governance, Risk, Controls and Assurance Practices — rbi.org.in
- RBI’s discussion paper on digital-payment fraud safeguards — rbi.org.in
- Complainant checklist — cybercrime.gov.in