DPDP Act Consent Manager Registration India: Insurance API Impact
DPDP Act consent manager registration in India is now available under a phased framework. See what it means for insurance APIs, fintech consent flows, partners and audit trails.
Article brief
17 November 2026
15 min read
By Bharatsure Team
Category
Insurance infrastructure
Share
LinkedInQuick answer
India’s Consent Manager registration framework took effect on 13 November 2026, with eligible Indian companies able to apply through the online portal launched on 14 November 2026. For insurers, brokers, lenders and embedded-insurance platforms, the immediate task is to separate a registered Consent Manager’s role from each partner’s own data responsibilities and prepare consent-aware API and vendor workflows before the wider DPDP requirements take effect on 13 May 2027.
- The Data Protection Board of India assesses Consent Manager applications under the registration framework. MeitY’s 14 November 2026 announcement says eligible Indian companies can apply and prepare to offer consent-management services; it does not establish that registered Consent Managers are already providing the full statutory service.
- A registered Consent Manager gives people an interoperable way to give, manage, review and withdraw consent. It does not remove an insurer, broker, lender or platform’s accountability for processing it controls.
- Insurance API integrations should be designed to record the notice, purpose, consent state, withdrawal event, recipient and processing decision, while keeping consent records distinct from policy, servicing and claims records.
- The wider DPDP requirements covering Data Principal rights, Data Fiduciary obligations and Board inquiry and penalty processes are scheduled to take effect on 13 May 2027. Teams should use the intervening period to redesign customer journeys, contracts and technical controls.
For DPDP Act consent manager registration in India, the practical answer for insurance and financial-services teams is clear: a registered Consent Manager can become an interoperable consent channel, but it does not take over the insurer, broker, lender, fintech or platform’s responsibility for the customer data processing it determines. The registration framework took effect on 13 November 2026, and MeitY announced an online application portal on 14 November 2026. The wider provisions on Data Principal rights and Data Fiduciary obligations are scheduled to take effect on 13 May 2027, so partners should now map consent capture, API permissions, withdrawal propagation, vendors and evidence before they connect a Consent Manager to policy issuance, lending-linked cover, servicing or claims journeys. MeitY’s announcement on the registration framework sets out the current position.
DPDP Act consent manager registration in India: what the update says
A Consent Manager is a registered entity that enables a Data Principal, the individual whose personal data is processed, to give, manage, review and withdraw consent through an accessible, transparent and interoperable platform. The Digital Personal Data Protection Rules, 2025 brought Rule 4, the registration rule, into force one year after their notification, making 13 November 2026 the key date for this part of the framework. The Rules’ commencement clause and Rule 4 provide the legal basis.
This is not a direction for every insurance distributor or financial-services platform to outsource its consent interface. It is a regulated route for a company that wants to act as a Consent Manager. The DPDP Act provides for a Data Principal to give, manage, review or withdraw consent through one, while every Consent Manager must be registered with the Board. The wider statutory consent arrangements are scheduled to take effect on 13 May 2027, while Rule 4’s registration framework is already in force. Section 6 of the DPDP Act, 2023 and MeitY’s implementation announcement distinguish the two stages.
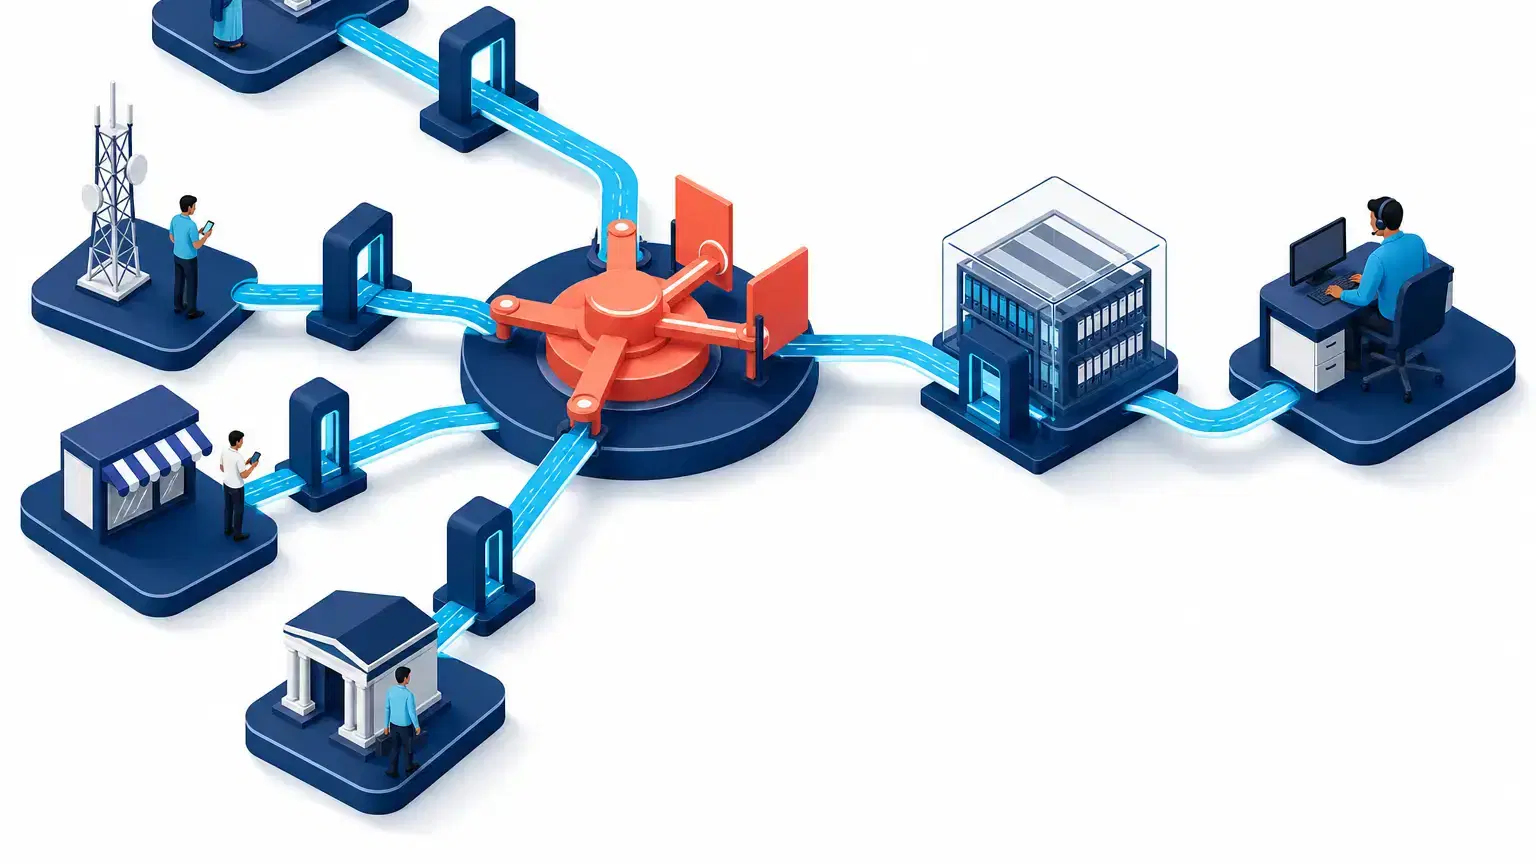
For an embedded insurance programme, this means a customer may eventually see consent requests associated with several parties: the checkout or lender platform, an insurer, a broker or distribution partner, a claims or servicing provider, and potentially a Consent Manager. The technical design should make each party’s role and each requested purpose understandable instead of reducing the journey to one generic privacy acceptance. This is a recommended future-state design based on the consent and notice framework in the DPDP Act, whose relevant rights and obligations are scheduled to apply on 13 May 2027.
Who approves consent managers in India and what remains to be verified
The Data Protection Board of India is the DPDP consent manager approval authority. An eligible applicant applies to the Board with the particulars, information and documents that the Board publishes. The Board may make inquiries, register an applicant and publish its particulars, or reject the application and communicate its reasons. MeitY’s 14 November 2026 release also states that eligible companies can apply through the newly launched online portal and that the register will be publicly available on the Board’s website. Rule 4 and MeitY’s portal announcement describe that route.
The baseline eligibility is substantial. The applicant must be an Indian-incorporated company, have sufficient technical, operational and financial capacity, sound finances and fit management, and maintain net worth of at least ₹2 crore. It also needs independent certification of an interoperable platform against the Board’s published data-protection standards and assurance framework, along with appropriate technical and organisational measures. Part A of the First Schedule to the Rules lists these conditions.
The operating detail matters as much as the application. Before treating a provider as a registered Consent Manager, procurement and compliance teams should confirm its entry on the Board’s published register, the Board’s applicable technical standards and assurance framework, the provider’s supported consent and withdrawal flows, and its controls for conflicts of interest. The Rules require a Consent Manager to avoid conflicts with Data Fiduciaries and to publish specified ownership and management information. Part B of the First Schedule is the relevant source for those obligations.
How consent managers may affect insurance API data flows
Architecturally, a Consent Manager is best treated as an orchestration layer for the customer’s consent decision rather than as a readable insurance-data store. The Rules require the manner of making personal data available or sharing it to ensure that its contents are not readable by the Consent Manager. They also require records of consents given, denied or withdrawn, notices associated with consent requests and sharing with a transferee Data Fiduciary. This points towards separating consent records and routing functions from readable policy, servicing and claims data. It does not, by itself, state a blanket prohibition on every form of data storage by the Consent Manager. These obligations sit in the future-state Rules that are scheduled to apply on 13 May 2027. The Consent Manager obligations in the First Schedule should shape API architecture now.
For example, a lender may offer credit-linked personal accident cover at loan disbursal. A consent-aware flow can send the customer a specific request for the processing needed to issue and service that cover. The consent record should identify the lender or platform, insurer, any recipient Data Fiduciary, the purpose, data fields or categories, notice version and the decision. If consent is withdrawn after the relevant provisions commence, the workflow should determine what processing must stop, what processing can continue because it is authorised or required by another law, and which processors need the instruction. Sections 5 and 6 of the DPDP Act and the MeitY implementation timetable support this future-state approach.
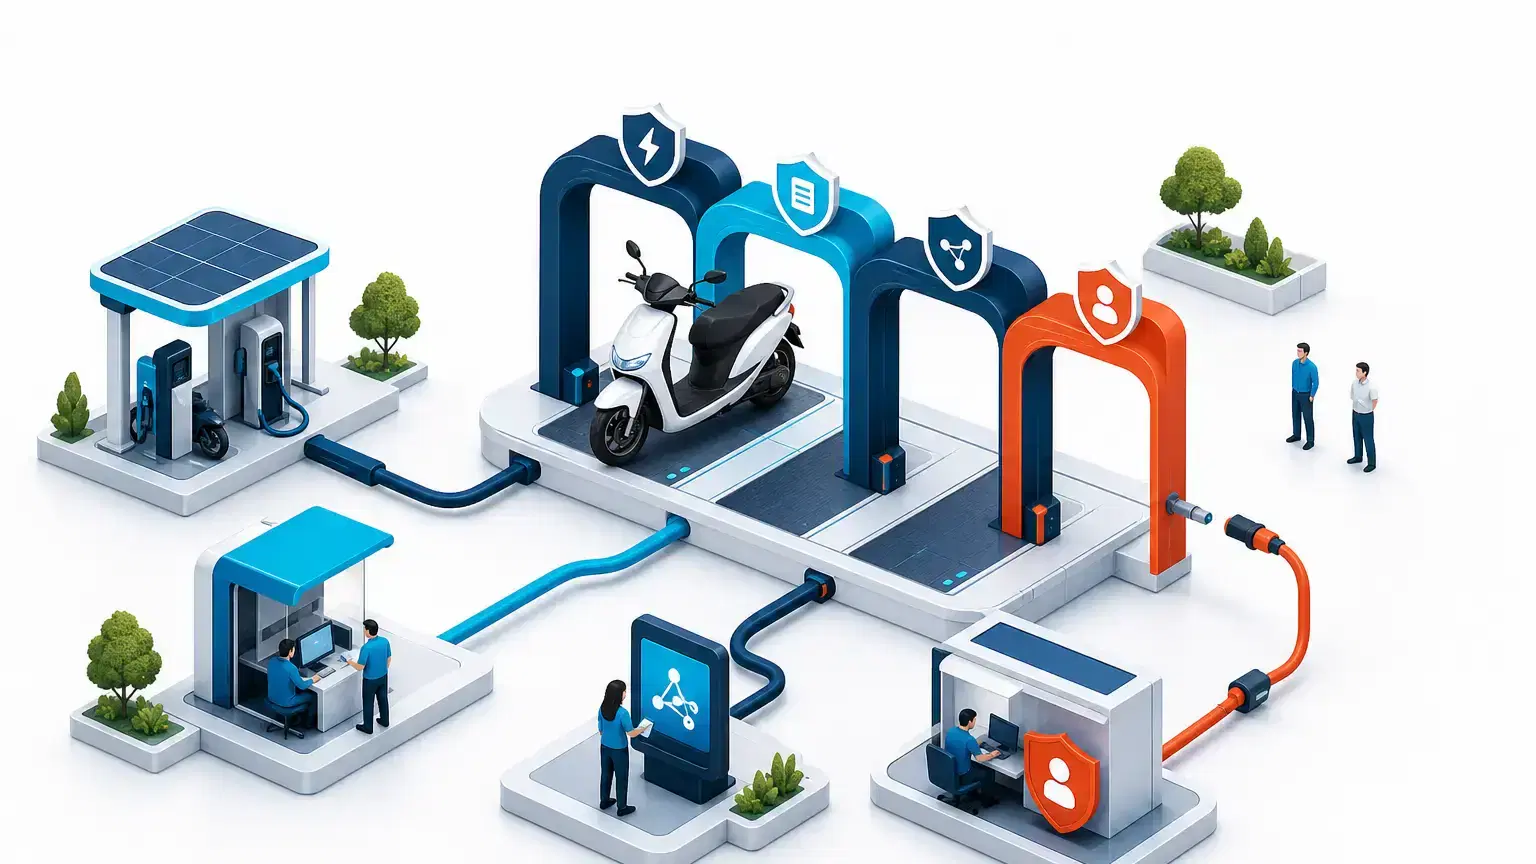
This is particularly relevant where an insurance API passes customer information between a platform, insurer, servicing partner and claims administrator. Build a permission check before each onward disclosure or purpose change, not only at onboarding. Systems supporting insurance API infrastructure for partner integrations should carry a stable consent reference alongside the policy, application or claim reference without using that reference as a substitute for purpose-specific controls. This is an implementation recommendation for the scheduled DPDP framework, not a statement that every cited statutory duty is already operative.
Consent capture, purpose limitation and withdrawal: a partner checklist
The DPDP Act describes consent as free, specific, informed, unconditional and unambiguous, expressed through clear affirmative action, and limited to personal data necessary for the specified purpose. It also describes clear and plain-language consent requests, access in English or a language in the Eighth Schedule to the Constitution, and withdrawal that is as easy as giving consent. These requirements are future-state provisions scheduled to take effect on 13 May 2027. Sections 5 and 6 of the DPDP Act and MeitY’s implementation announcement set out the relevant timing.
Use the following checklist for insurance data consent management in India:
- Separate purposes. Design the future-state journey so policy issuance, policy servicing, claims administration, fraud review, cross-sell marketing and sharing with another group entity are not combined into one unexplained choice. Match each request to a defined customer outcome and the data needed for it. Sections 5 and 6 of the DPDP Act provide the statutory direction for this design, scheduled for 13 May 2027.
- Version the notice. Keep the rendered notice, language, purpose, data description, user action, timestamp and channel. Once the relevant provisions commence, the Data Fiduciary will bear the burden of proving that it gave notice and received consent where consent is the processing basis. Section 6(10) of the DPDP Act makes this evidence a key future-state control.
- Make withdrawal operational. Build a withdrawal event that can reach API gateways, campaign tools, CRM systems, insurer interfaces and downstream processors that rely on that consent. Once operative, the Act provides for the Data Fiduciary to cease, and cause its Data Processors to cease, processing within a reasonable time unless processing without consent is otherwise authorised or required by law. Section 6(6) of the DPDP Act explains the future-state rule.
- Distinguish retention from marketing use. A consent withdrawal may end a particular consent-based use, but it does not automatically override a retention obligation under another applicable law. Create a retention map by record type, including proposal, policy, payment, servicing and claims evidence.
- Test the customer view. Build a customer view that can show a meaningful consent history and support withdrawal and rights channels without requiring the customer to navigate several partner apps. The wider Data Principal rights are scheduled to take effect on 13 May 2027. Sections 11 to 13 of the DPDP Act and MeitY’s implementation announcement provide the timing.
The detailed Rules on notice, security safeguards, breach intimation and rights mechanisms are scheduled to come into force on 13 May 2027. That timetable does not make early design work optional for complex ecosystems. The Rules’ staged commencement provisions and MeitY’s implementation update provide the dates.
What insurers, lenders and platforms should change in their integration design
First, establish a processing-role map for every journey. For an embedded policy offered during a loan, purchase or workforce onboarding flow, identify who determines the purpose and means of each processing activity, who processes on another party’s behalf, and who receives data as a separate Data Fiduciary. The DPDP Act sets out that a Data Fiduciary is responsible for compliance for processing undertaken by it or on its behalf by a Data Processor, and can engage a processor only under a valid contract. These are future-state statutory obligations scheduled to take effect on 13 May 2027. Section 8 of the DPDP Act and MeitY’s implementation announcement set out the staged position.
Second, design APIs around events and proof. Use consent status and purpose identifiers at the point of quote, issuance, endorsement, renewal, customer support and claims hand-off. Keep an immutable event trail showing the service request, consent validation result, decision, recipient and response. The Consent Manager’s mandated record does not remove the partner’s need to retain evidence of its own notice and processing decision once the relevant provisions apply. The First Schedule to the Digital Personal Data Protection Rules, 2025 and Section 6 of the DPDP Act support this design.
Third, make vendor contracts precise. Define the permitted processing instructions, data categories, security measures, sub-processing position, withdrawal and deletion hand-offs, breach escalation, audit support and return or deletion requirements. The Rules set out reasonable safeguards for processing under a Data Fiduciary’s control, including contractual provisions with Data Processors where applicable. These requirements are scheduled to apply on 13 May 2027. Rule 6 of the Digital Personal Data Protection Rules, 2025 and the Rules’ commencement clause support this contractual focus.
Finally, keep consent systems connected to the service experience. A withdrawal from optional marketing should not accidentally block a valid policy servicing request. Equally, a consent record should not cause teams to overlook the customer’s separate access, correction, erasure and grievance rights. The Act provides for information about processing and the identities of Data Fiduciaries and Data Processors with which data has been shared, subject to stated exceptions. These Data Principal rights are scheduled to take effect on 13 May 2027. Sections 11 to 13 of the DPDP Act and MeitY’s implementation announcement explain the customer-facing framework and timing.
Questions to ask before selecting or integrating a consent manager
Ask the provider to show its registration status and explain the scope of services that its product supports. A consent-management product is not necessarily a registered Consent Manager, and a partner should not describe it as one without confirming the Board’s registration. Rule 4 of the Digital Personal Data Protection Rules, 2025 provides the registration route that is in force from 13 November 2026.
Then test the integration against real insurance flows:
- Can the platform preserve the insurer or lender’s own notice and purpose language, including regional-language options where required under the future-state framework?
- Does each consent decision produce a machine-readable, exportable record with a notice version and timestamps?
- Can withdrawal reach every relevant internal tool and contracted processor, with a traceable completion status once the relevant provisions commence?
- Does the API prevent data disclosure where the purpose, recipient or consent state does not match the request?
- Can the Consent Manager avoid reading the contents of shared customer data, as the Rules require?
- What is the incident process, including the data fields supplied to the partner for its own breach response and customer communication?
- How are conflicts of interest, ownership disclosures and changes in control governed?
- What happens to consent records, open policies, active claims and customer support if the integration ends?
The consent, notice, withdrawal and rights controls in these questions should be treated as preparation for the wider framework scheduled to take effect on 13 May 2027. The staged commencement provisions in the Rules and MeitY’s implementation announcement provide the timetable. These questions are especially important for embedded insurance distribution, where consent can be collected at a high-volume customer moment, and for claims and servicing data workflows, where the information required after a policy is issued may be different from the information required to present or issue cover.
DPDP consent-manager FAQ for insurance and fintech teams
Does a Consent Manager become responsible for all insurance data processing?
No. A Consent Manager has its own statutory role and obligations to the Data Principal, but the entity that determines the purpose and means of a processing activity is treated as the Data Fiduciary for that activity. An insurer, lender, broker or platform should therefore maintain its own purpose map, notice records, processor governance and security controls. The relevant statutory separation is part of the wider framework scheduled to take effect on 13 May 2027. Sections 6 and 8 of the DPDP Act and MeitY’s implementation announcement set out the position.
Can a partner use a Consent Manager for a claim or servicing journey?
It may support consent decisions that are relevant to the journey, but the integration should be purpose-specific. Claims and servicing can involve different data types, recipients and legal retention needs from onboarding or marketing. The partner should document the relevant processing basis and customer communication for each use rather than reusing a broad consent captured at policy purchase. The notice and consent framework described in the DPDP Act is scheduled to apply on 13 May 2027, so this is a recommended preparation step.
What audit records should a registered Consent Manager keep?
Once the applicable First Schedule provisions commence, it must retain records of consents given, denied and withdrawn, notices that preceded or accompanied consent requests, and data sharing with a transferee Data Fiduciary. It must make the record accessible to the Data Principal and retain it for at least seven years, subject to longer agreed or legal requirements. Part B of the First Schedule to the Rules contains those future-state requirements, while Rule 4’s registration framework is already in force.
What should a fintech do before adding insurance offers to its app?
Map the customer journey from offer display through issuance, servicing, renewals and claims. Identify each API recipient, document the specific purpose for every customer-data transfer, separate necessary service processing from optional marketing, and build tested withdrawal propagation. The product team should also align disclosures and data handling with applicable financial-sector and insurance requirements, which can sit alongside the DPDP framework. The DPDP rights and Data Fiduciary duties discussed in this article are scheduled to take effect on 13 May 2027. MeitY’s implementation announcement provides the relevant timetable.
Consent-aware infrastructure needs to work across the whole customer journey, not just at a checkbox. Product and compliance teams can Book a demo to map consent-aware insurance API, servicing and claims workflows across their customer journey. Implementation must be aligned with the applicable law, rules and each partner’s responsibilities.
Frequently asked questions
Who approves Consent Managers under the DPDP framework?
The Data Protection Board of India assesses applications and may register an applicant or reject it with reasons. The Board may also seek further information and, after an opportunity to be heard, can direct corrective measures or suspend or cancel a registration where the prescribed conditions and obligations are not met. Rule 4 of the Digital Personal Data Protection Rules, 2025 sets out that process.
Must an insurer, broker, fintech or lender become a registered Consent Manager?
No general registration requirement is created merely because a business captures consent for its own insurance, lending or platform journey. Registration is for an entity acting as the statutory Consent Manager. The DPDP Act provides for a Data Principal to give, manage, review or withdraw consent through a Consent Manager, while the Data Fiduciary remains responsible for its own processing and for processing carried out on its behalf by a Data Processor. These statutory arrangements are part of the wider framework scheduled to take effect on 13 May 2027. Sections 6 and 8 of the DPDP Act, 2023 and MeitY’s implementation announcement explain the staged position.
What should be stored for a consent-linked insurance API call?
Design the system to store an auditable consent decision connected to the relevant notice version, stated purpose, data categories, customer identifier, recipient, timestamp, event source and subsequent withdrawal or denial. Once the relevant Rules apply, a registered Consent Manager must retain records of consent activity, notices and sharing with a transferee Data Fiduciary, and provide access to those records for at least seven years. The insurance partner should also retain evidence needed to demonstrate its own lawful processing and meet any separate statutory retention requirement. The First Schedule to the Digital Personal Data Protection Rules, 2025 and Section 6 of the DPDP Act support this future-state design.
When do the wider DPDP operational requirements apply?
The Consent Manager registration framework came into effect on 13 November 2026. MeitY has stated that other key provisions covering Data Principal rights, Data Fiduciary obligations and the Board’s inquiry and penalty processes are scheduled to take effect on 13 May 2027. MeitY’s 14 November 2026 announcement should be read alongside the staged commencement in the Digital Personal Data Protection Rules, 2025.
Sources
- MeitY’s announcement on the registration framework — pib.gov.in
- The Rules’ commencement clause and Rule 4 — meity.gov.in
- Section 6 of the DPDP Act, 2023 — meity.gov.in