RBI Digital Fraud Compensation 2027: A Fintech Readiness Plan
A readiness plan for RBI digital fraud compensation in 2027, covering complaint intake, evidence, customer communication and insurance hand-offs.
Article brief
7 November 2026
13 min read
By Bharatsure Team
Category
Insurance infrastructure
Share
LinkedInQuick answer
RBI’s final directions apply to specified electronic banking transactions undertaken on or after January 1, 2027. This guide maps the complaint, evidence and communication decisions that banks and fintech partners should make without treating bank-led redress and insurance claims as the same process.
- RBI’s amended directions apply to relevant electronic banking transactions undertaken on or after January 1, 2027. Each fintech should confirm the applicable bank category, bank policy and partnership agreement.
- Complaint journeys need reliable transaction, alert, reporting and acknowledgement timestamps. Reporting within five calendar days is material to zero liability in qualifying third-party-breach cases.
- The small-value mechanism applies to a bona fide individual or sole proprietor whose fraudulent EBT complaint is covered by the customer-negligence provision, involves gross loss of up to ₹50,000, and meets the reporting and other conditions. It provides 85% of net loss or ₹25,000, whichever is lower, once in a lifetime.
- Bank reversal or compensation and an insurance claim are separate outcomes. Support scripts and workflow statuses should not describe them as interchangeable.
The RBI digital fraud compensation in 2027 framework should be treated as an operating-readiness priority, not as a blanket promise of payment to every fraud complainant. The Reserve Bank of India issued final amendment directions on June 24, 2026, effective for relevant electronic banking transactions undertaken on or after January 1, 2027. Banks, fintechs, neo-banks and payment platforms need complaint intake, evidence, communication and escalation workflows that reflect the bank-led decision process and keep insurance claims separate. RBI’s June 24, 2026 press release
What is known about RBI digital fraud compensation in 2027, and what still needs confirmation
The final directions cover commercial banks, small finance banks, payments banks, local area banks, regional rural banks, urban co-operative banks and rural co-operative banks. The RBI issued separate amendment instruments for these categories, with the changes taking effect from January 1, 2027. RBI’s June 24, 2026 press release
For commercial banks, a fraudulent electronic banking transaction, or fraudulent EBT, includes an EBT carried out by a third party using fraudulently obtained credentials, an EBT approved by a customer under coercion or duress, and an unauthorised EBT. The direction also recognises that a third-party breach may involve an intermediary, including a Third-Party Application Provider, payment aggregator, payment gateway or telecom service provider. Commercial-bank amendment directions
For commercial-bank customers, the small-value mechanism applies only to a complaint involving a fraudulent EBT covered by paragraph 76N, which addresses fraud arising from customer negligence. The claimant must be a bona fide individual or sole proprietor, the complaint must involve gross loss of up to ₹50,000, and the customer must report the fraudulent EBT to both the bank and the National Cyber Crime Reporting Portal or helpline 1930 within five calendar days of its occurrence. Where those conditions are met, the compensation is 85% of net loss or ₹25,000, whichever is lower, available once in the person’s lifetime. The mechanism is payable only for losses from fraudulent EBTs occurring up to one year from the January 1, 2027 effective date. Commercial-bank amendment directions
The amount is therefore not a standard payout for every fraud complaint or every customer-negligence case. The bank must examine the complaint, establish liability, assess whether the loss is bona fide under its policy, and determine whether the conditions for compensation are met. Customer copy and workflow rules should describe the mechanism as conditional rather than automatic. Commercial-bank amendment directions
Each fintech should also establish which regulated bank owns the account, card or transaction relationship, which direction applies to that bank category, and what the bank’s board-approved policy and partnership agreement require. The RBI directions set the framework, while a fintech’s escalation duties, service levels and communication authority depend on its role in the transaction chain. Commercial-bank amendment directions
What fintech and banking partners should verify in the RBI primary source
A readiness review should begin with the direction that applies to the partner bank. Commercial banks and payments banks have separate amendment instruments, even where the core customer-protection approach is similar. Teams running programmes across bank categories should compare the commercial-bank directions with the payments-bank directions.
Verify these points before changing customer copy or operational policy:
- Transaction and customer scope: Confirm whether the payment is an EBT under the relevant direction and whether the complainant is the bank’s customer.
- Fraud classification: Separate bank negligence or deficiency, third-party breach, unauthorised activity and customer negligence. The bank bears the burden of proving customer liability. Commercial-bank amendment directions
- Reporting clock: Confirm what records the date of occurrence, when the bank received the complaint, and whether the customer has reported through the prescribed cybercrime route where relevant.
- Resolution clock: The bank’s policy may specify a shorter period, but its response may not exceed 45 calendar days from receipt of a domestic fraudulent-EBT complaint or 60 calendar days for a cross-border complaint. Commercial-bank amendment directions
- Small-value mechanism: Check that the case falls within the customer-negligence provision referenced by the mechanism, the claimant is an eligible individual or sole proprietor, gross loss is no more than ₹50,000, the loss is bona fide, both reporting routes were used within five calendar days, and the customer has not previously used the once-in-a-lifetime benefit. For an eligible case, compensation is 85% of net loss or ₹25,000, whichever is lower. The ₹25,000 figure is a cap, not a standard payout, and the mechanism applies only to qualifying losses occurring within one year of January 1, 2027. Commercial-bank amendment directions
- Customer communication: Confirm who can communicate classification, reversal, compensation, rejection reasons and supporting details.
- Record retention and reporting: Identify which records the bank needs from the fintech for investigation, audit, board reporting and any reimbursement process.
Digital-fraud complaint intake: timestamps, channels and escalation ownership
The directions make timestamp quality an operating control. Banks must provide 24x7 reporting access through channels such as phone banking, SMS, instant messaging, email, IVR, a toll-free helpline and branch reporting. They must provide a direct reporting link on their website and mobile application, where available, record alert-delivery and customer-response times, and issue an immediate acknowledgement carrying the complaint number and receipt timestamp. Commercial-bank amendment directions
A fintech that receives the first customer contact should capture, without delaying escalation:
- transaction ID, UTR or other payment reference;
- transaction date, time, amount and channel;
- payer and beneficiary identifiers available to the platform;
- when the customer discovered the incident;
- when and how the customer contacted the fintech and bank;
- the bank complaint number and acknowledgement time;
- the cybercrime complaint reference, if available;
- screenshots, messages, phone numbers, URLs and other fraud artefacts;
- the customer’s chronological account of events; and
- immediate protective actions already taken.
Ownership must be explicit. The fintech can guide the customer, preserve evidence and send structured information to the bank. The bank examines the complaint, establishes liability and issues the response required under the direction. An insurer or claims partner has a separate role in assessing a claim under the issued policy. Commercial-bank amendment directions
Create distinct queues for account security, bank complaint ageing, missing evidence and insurance claim servicing. One undifferentiated fraud ticket can obscure the organisation responsible for the next action.
How a complaint deadline changes customer journeys and operational SLAs
The five-calendar-day condition should shape the front end of the journey. It is expressly relevant to zero liability and reversal for a qualifying third-party breach reported to the bank within five calendar days of occurrence. For reports made after five calendar days in those third-party-breach cases, customer liability is determined under the bank’s policy. Bank negligence or deficiency is treated separately: the direction provides for zero liability and reversal irrespective of whether the customer reports the transaction. Commercial-bank amendment directions
The small-value compensation mechanism also requires the customer to report the fraudulent EBT to the bank and to the National Cyber Crime Reporting Portal or helpline 1930 within five calendar days of occurrence. It is available only for qualifying fraudulent EBT cases covered by the customer-negligence provision, subject to the claimant, loss, bona fide assessment, lifetime-use and time-limited eligibility conditions. Commercial-bank amendment directions
For teams interpreting the digital fraud complaint deadline in India, customer-facing journeys should prioritise immediate action:
- Secure access: Help the customer block or restrict affected payment instruments and review recent activity.
- Report to the bank: Deep-link, transfer or route the customer to the bank’s recognised complaint channel.
- Preserve acknowledgement: Store the complaint number, date, time and channel used.
- Guide cybercrime reporting: Explain the National Cyber Crime Reporting Portal and helpline 1930 route without representing it as an automatic payment trigger.
- Collect evidence: Prefill transaction data where permitted and let the customer correct it.
- Explain next steps: Distinguish investigation, bank reversal or compensation, recovery and any insurance claim.
Internal SLAs should be much shorter than regulatory maxima. Route a suspected-fraud complaint to the bank in minutes rather than days, and track first response, bank hand-off, acknowledgement, missing evidence and case age separately.
Compensation, bank liability and insurance cover are different customer outcomes
The RBI framework can lead to different bank-side outcomes. A customer may receive reversal where bank negligence or deficiency is established, zero liability after timely reporting of a qualifying third-party breach, a decision on the small-value mechanism where its conditions are met, or a reasoned rejection where customer liability is established. For credit-card fraudulent EBT complaints requiring reversal, the bank must provide shadow reversal within five calendar days of notification. Commercial-bank amendment directions
Insurance is a separate contract. An embedded policy may cover only defined events, subject to its terms, conditions, limits, exclusions, reporting duties and evidence requirements. Product wording should identify the covered fraud methods and payment types instead of relying on a broad protection label. BharatSure’s embedded cyber and fraud cover can be considered alongside, not in place of, the bank’s fraud-resolution process.
Customer communication should avoid one blended reimbursement status. Use distinct labels such as:
- bank complaint submitted;
- bank investigation in progress;
- provisional or shadow reversal applied;
- bank liability decision issued;
- small-value compensation application requested;
- insurance claim intimated;
- insurance documents required; and
- insurance claim decision issued.
If funds are recovered after compensation has been paid, the customer’s bank must recalculate the compensation using net loss and make the prescribed adjustment from the recovery. Insurance documentation should separately address how bank payments, recoveries and other indemnities affect any policy payment. Commercial-bank amendment directions
Designing UPI-fraud protection alongside a bank’s fraud-resolution process
Effective UPI fraud protection for fintechs should begin with event definitions, not the payment rail. A customer may deny making a payment, approve it after deception, share credentials, act under coercion or make an error without fraud. The bank and insurer may classify the same facts differently because they apply separate frameworks.
The product team should map each scenario across four questions:
- What must the bank do under its complaint and liability framework?
- What must the fintech do under its agreement with the bank?
- Does the insurance wording define the event as covered?
- What evidence can support both processes without merging their decisions?
The guide to UPI fraud insurance design for fintechs can help teams distinguish authorised-transfer scams, unauthorised transactions and customer errors. The issued policy should state which events may be covered and which conditions apply.
An embedded fraud-insurance programme can use a shared intake layer while maintaining separate downstream records. AffinityOS insurance API infrastructure can support structured programme records, while claims infrastructure for partner programmes can support claim intimation, document collection, status updates and insurer or TPA hand-offs.
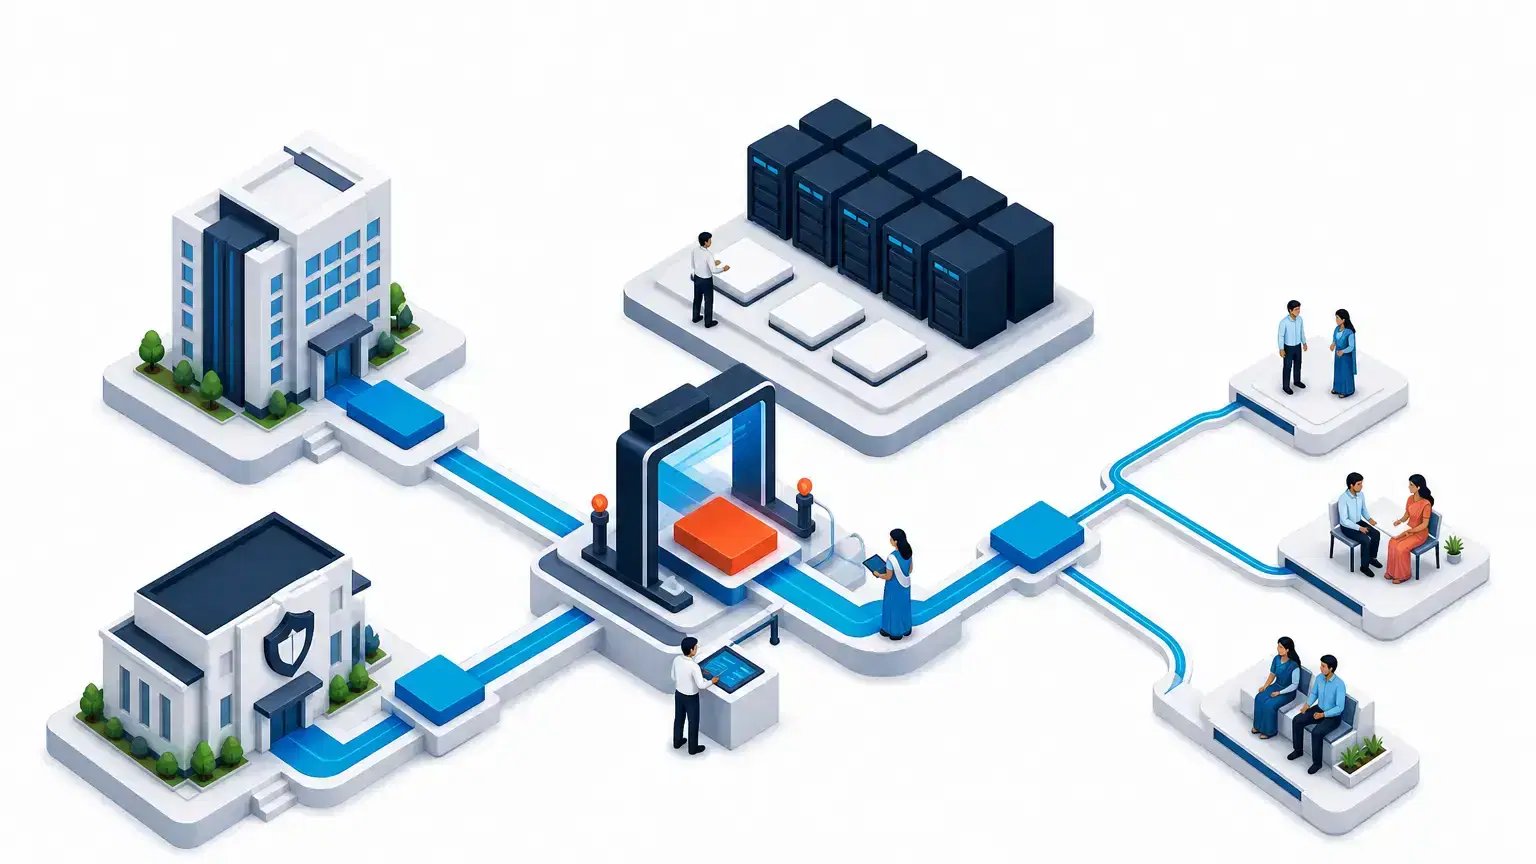
A practical data model uses a parent incident ID with linked child references for the platform support case, bank complaint, cybercrime report and insurance claim. Each child record should have its own owner, status, deadline, evidence set and decision source.
FAQ: Can a fintech promise compensation for every digital-fraud complaint?
Can a fintech promise compensation for every digital-fraud complaint?
No. The bank must establish the complaint’s classification, customer liability and eligibility under the applicable RBI direction and bank policy. The small-value mechanism is conditional and capped. An insurance claim is also assessed independently under the policy terms. Commercial-bank amendment directions
Does the five-calendar-day condition apply to every possible outcome?
No. It applies expressly to zero liability in qualifying third-party-breach cases reported to the bank within five calendar days. It is also a condition of the small-value compensation mechanism for eligible fraudulent EBT cases covered by the customer-negligence provision, along with the required cybercrime reporting and other conditions. Bank negligence or deficiency has separate zero-liability treatment under the direction. Commercial-bank amendment directions
Can one customer-facing case number cover the whole journey?
A parent case number can help the customer navigate the process, but the bank complaint, cybercrime report and insurance claim should retain separate references. This protects audit trails and prevents a bank status from being mistaken for an insurer decision.
What happens when a customer disputes the bank’s response?
After first raising the matter with the regulated entity, a customer may use the applicable RBI escalation route where the complaint meets the scheme’s conditions. The RBI Integrated Ombudsman Scheme FAQ, updated July 1, 2026, explains the complaint channels and maintainability requirements. A fintech can direct the customer to the appropriate route but should not present itself as the decision-maker.
A pre-2027 readiness checklist for embedded fraud-protection programmes
Use the implementation period to test the whole operating chain:
- Identify every bank category, payment rail, app and intermediary involved in the programme.
- Obtain the partner bank’s approved fraud-complaint policy and agreed implementation specifications.
- Map bank negligence, third-party breach, unauthorised activity and customer-negligence scenarios.
- Define when the fintech creates a support case and when it transmits a complaint to the bank.
- Capture transaction, alert, discovery, reporting and acknowledgement timestamps.
- Confirm round-the-clock escalation coverage and named fallback owners.
- Build separate statuses for bank resolution, small-value compensation and insurance claims.
- Review product and marketing copy for unconditional compensation language.
- Align insurance wording with the fraud scenarios described in the customer journey.
- Define evidence fields once, then share them only with authorised stakeholders.
- Test duplicate reports, partial recoveries, multiple beneficiary banks and cross-border cases.
- Reconcile bank reversals, compensation, recoveries and insurance payments without duplicate payment.
- Train customer-support teams to explain the distinct roles of the bank, cybercrime-reporting system and insurer.
- Run simulations for complaints received on weekends, holidays and near the five-day boundary.
- Measure hand-off time, acknowledgement time, missing evidence, complaint age and claim age independently.
The objective is not another fraud form. It is an incident workflow that moves quickly, preserves evidence and tells customers which organisation is responsible for the next decision.
Book a demo to map a customer-facing fraud-protection programme to your onboarding, transaction and claims workflows, while keeping bank complaint handling and insurance claims clearly separated.
Frequently asked questions
Can a fintech promise compensation for every digital-fraud complaint?
No. The bank must examine and classify the complaint under the applicable RBI direction and its policy. The small-value mechanism applies only where its specified conditions are met and is capped. Any insurance claim is assessed separately under the issued policy terms, conditions, limits, exclusions and evidence requirements.
Does the five-calendar-day condition apply to every possible outcome?
No. It is expressly relevant to zero liability for qualifying third-party breaches reported to the bank within five calendar days. It is also a condition of the small-value compensation mechanism, which applies to eligible customer-negligence cases, along with reporting through the National Cyber Crime Reporting Portal or helpline 1930 and the other conditions in the applicable direction.
Can a fintech use one case number for the bank complaint and insurance claim?
A parent customer-facing case can coordinate the journey, but the bank complaint, cybercrime report and insurance claim should retain separate references, statuses, owners and decision records.
Sources
- RBI’s June 24, 2026 press release — rbi.org.in
- Commercial-bank amendment directions — rbi.org.in
- Payments-bank directions — rbi.org.in
- RBI Integrated Ombudsman Scheme FAQ — rbi.org.in