NBFC Cyber Fraud Insurance: Controls After Loan Diversion
NBFC cyber fraud insurance can support recovery after loan diversion, but lenders first need controls for approval, disbursal, access, evidence and partner workflows.
Article brief
19 November 2026
14 min read
By Bharatsure Team
Category
Insurance infrastructure
Share
LinkedInQuick answer
A reported Delhi-NCR incident involving alleged AI-assisted loan diversion is a prompt for NBFCs, fintechs and embedded-finance partners to review approval-to-disbursal controls. This guide explains what to verify before publishing incident details, how cyber and fraud policies may respond, and which operational controls, evidence workflows and partner responsibilities should be ready.
- Treat reported loan-diversion details as allegations until the lender, law-enforcement record or other primary evidence confirms them.
- Review the full approval-to-disbursal chain, including beneficiary changes, privileged access, API calls, employee actions and partner controls.
- Cyber or fraud insurance may support certain covered losses and response costs, but coverage depends on the policy wording, exclusions, conditions and evidence.
- Prepare a coordinated response workflow covering containment, regulatory reporting, customer communication, evidence preservation, recovery and claim notification.
Loan diversion is not only a credit problem. It can involve identity compromise, manipulated borrower or beneficiary data, insider access, compromised APIs, weak maker-checker controls or a failure to detect unusual activity between sanction and disbursal. For teams assessing nbfc cyber fraud insurance, the first question is not whether a reported incident sounds plausible. It is whether the lender can establish what happened, when it happened, which control failed and which policy section, if any, could respond.
The article brief refers to a Delhi-NCR report alleging AI-assisted attacks and diverted approved loans. Those details should remain described as allegations until the affected lender, law-enforcement agencies, forensic investigators or another authoritative record confirms them. The operational response below is useful without treating the reported amount, method or identity of any NBFC as established fact.
What the reported NBFC loan-diversion incident could mean for lenders
A loan-diversion allegation should trigger a controlled fact-finding exercise rather than immediate public attribution. Product, risk, fraud, information-security, legal, compliance, operations and partnership teams should work from one incident record with a clear timeline.
Start by separating five questions:
- Was the loan genuinely approved? Check the credit decision, underwriting inputs, approval authority, override history and digital signatures.
- Was the disbursal authorised? Match the payment instruction to the approved borrower, permitted end use and recorded beneficiary.
- Was any data changed after approval? Review changes to bank-account details, mobile number, email address, address, repayment mandate, collateral information and loan purpose.
- Who or what made the change? Link the event to a user, service account, API client, device, IP address, batch job or partner system.
- What evidence supports the conclusion? Distinguish confirmed facts, technical indicators, working hypotheses and untested allegations.
The RBI's Fraud Risk Management Directions for NBFCs require a framework for prevention, early detection, investigation, staff accountability, monitoring, recovery and reporting. The same direction set also places responsibility on the NBFC's governance structure, which means a material incident should not remain only within a security or operations queue.
For digital lending arrangements, the RBI Digital Lending Directions, 2025 cover regulated entities, lending service provider arrangements, loan disbursal, servicing, repayment, data and technology requirements. A lender should therefore examine the controls operated by an LSP, fintech or embedded-finance platform, while retaining clear ownership of regulated lending responsibilities.
Does NBFC cyber fraud insurance cover diverted loan proceeds?
There is no universal answer. “Cyber insurance” may refer to several different protections, including incident response and restoration costs, privacy or security liability, business interruption, cyber extortion, funds-transfer fraud, social-engineering fraud or a separate crime policy. A diverted loan may involve more than one loss category, and the relevant cover may sit outside a standard cyber wording.
A lender reviewing cyber insurance for NBFCs should ask its broker and insurer to map the proposed event against:
- the insuring agreement that could respond;
- whether the insured loss is the lender's money, a customer's money, a partner's money or a liability to another party;
- whether the event is treated as unauthorised access, fraudulent instruction, impersonation, employee dishonesty, social engineering or an operational error;
- sub-limits, deductibles, waiting periods and aggregation provisions;
- exclusions for authorised transfers, voluntary payment, inadequate verification, known circumstances, internal acts or failure to follow controls;
- notification, cooperation, forensic-investigation and law-enforcement conditions; and
- recovery, subrogation and consent requirements.
The BharatSure cyber insurance product page describes cyber cover as an embedded product option for banks, NBFCs and fintechs. It should be treated as a starting point for product and distribution discussions, not as a promise that a particular diverted-loan loss will be paid. Cover, exclusions and claim decisions depend on the policy terms.
Insurance works best after the lender has defined the event taxonomy, preserved evidence and assigned responsibility. A policy cannot repair an approval workflow, reverse every payment or remove the need for regulatory and law-enforcement reporting.
Where AI-assisted attacks can exploit the loan approval-to-disbursal journey
AI can increase the speed, scale and plausibility of fraud attempts. It may help attackers produce convincing borrower communications, synthetic documents, voice impersonation, targeted phishing or automated probing of exposed interfaces. It can also help a criminal identify when a loan has been approved and then target the short interval before payment.
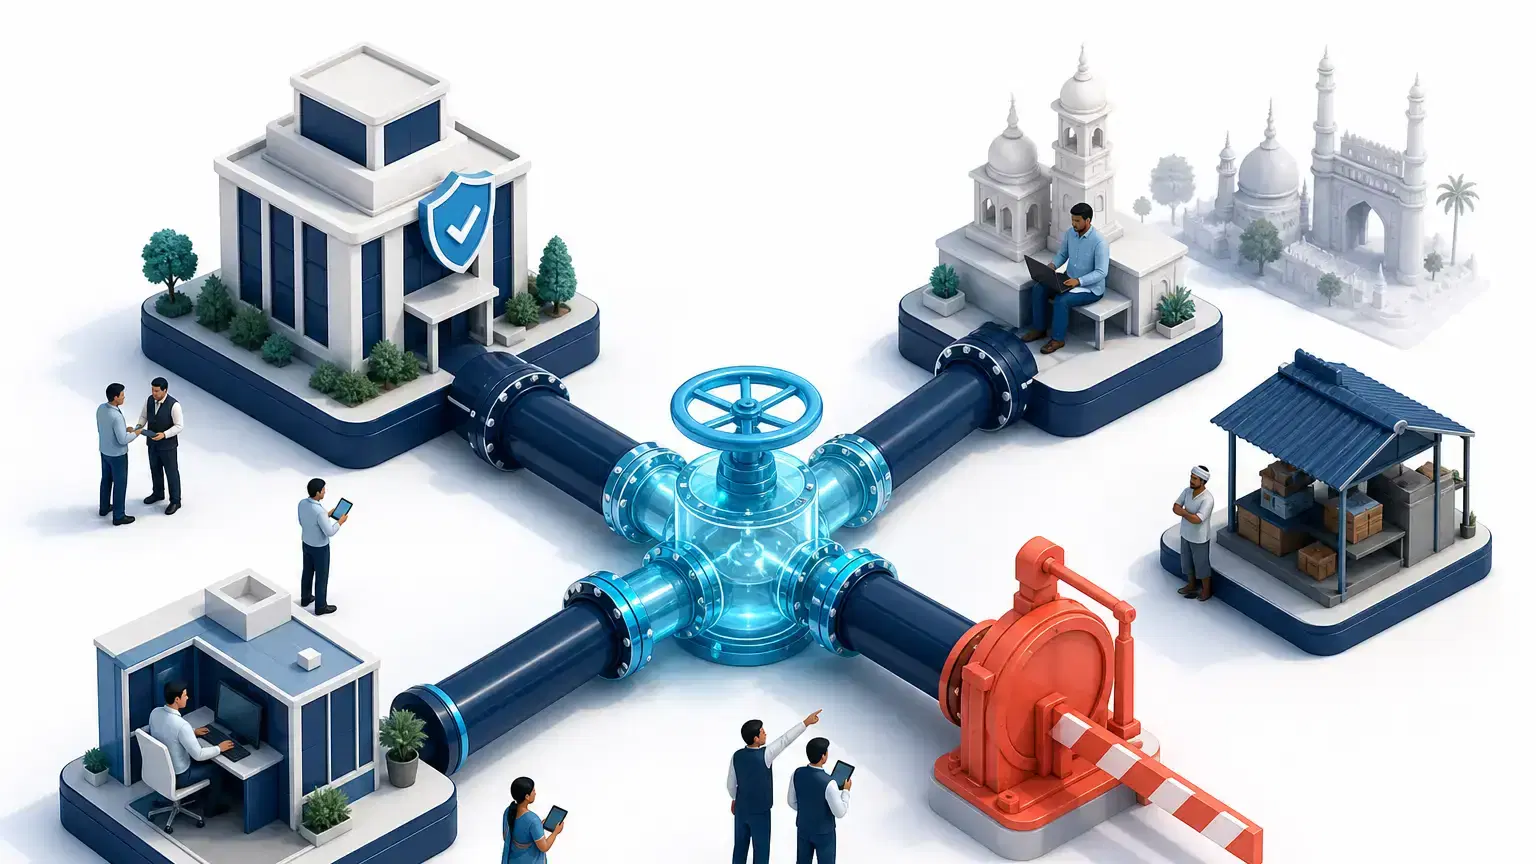
The risk is not limited to the credit decision engine. Review the complete chain:
- Acquisition and onboarding: synthetic identities, manipulated documents, compromised email or mobile numbers and repeated applications from linked devices.
- Underwriting: altered income evidence, coordinated applications, model-input manipulation, manual overrides and unusual concentration by device, employer, geography or beneficiary.
- Approval: excessive approval authority, weak step-up authentication, shared credentials and approval without independent confirmation of critical fields.
- Post-approval servicing: changes to bank accounts, repayment mandates, addresses or contact details made shortly before disbursal.
- Disbursal: API replay, token theft, batch-file manipulation, altered beneficiary records, weak bank-account validation or insufficient maker-checker review.
- Partner operations: broad LSP permissions, unclear ownership of logs, unmanaged service accounts, insecure webhooks and delayed escalation.
For AI fraud detection for lenders, the useful objective is not to label every unusual event as malicious. It is to identify high-risk combinations that justify a pause or second review, such as a new beneficiary plus a recent contact change, a privileged login from an unusual device, a sudden override followed by same-day disbursal, or multiple accounts linked to one technical fingerprint.
The lender should document which alerts block a transaction, which create a review queue and which are used only for investigation. Excessive false positives can encourage staff to bypass controls, while unexplained silent failures make later claims and audits harder to support.
Five controls to review across borrower, employee and beneficiary changes
1. Make critical-field changes high-friction
Treat changes to the borrower's bank account, beneficiary, mobile number, email, repayment mandate and loan purpose as high-risk events. Require re-authentication, independent confirmation and a cooling-off or review period where appropriate. A change should not automatically flow from a customer-facing interface into the payment instruction without validation.
2. Separate approval from payment release
The person or service that approves credit should not be able to change the beneficiary and release funds without an independent control. Use role-based access, dual authorisation, transaction limits and a clear exception process. Log the full sequence, not only the final approval status.
3. Secure privileged and service access
Review administrator accounts, API keys, service accounts, emergency access, token lifetimes, secrets storage, device binding and leaver access. Require phishing-resistant or strong multi-factor authentication for privileged actions where supported. Alert on unusual access patterns, privilege escalation, bulk changes and dormant-account use.
The RBI's NBFC cybersecurity directions require cybersecurity governance, a cyber crisis management plan, audit trails and controls covering threats such as identity fraud, business email fraud and password-related fraud. The directions also address third-party arrangements and information-security risk management.
4. Monitor beneficiary and payment behaviour
Build rules and models around the approval-to-payment interval. Useful signals include newly added accounts, mismatched account-holder names, unusual bank or branch patterns, rapid changes after approval, repeated use of one beneficiary across borrowers, failed validation attempts and payment instructions created outside expected operating hours.
Monitoring should connect customer, employee, device, API, bank-account and partner identifiers. A fragmented view can miss a coordinated pattern even when each individual transaction appears plausible.
5. Test partner controls, not only internal controls
For an LSP, fintech or embedded-finance platform, agree who owns beneficiary validation, fraud alerts, log retention, incident notification, customer communication and recovery actions. Test those responsibilities through a scenario exercise. The RBI's IT outsourcing directions for NBFCs emphasise need-to-know access, oversight of service providers, business continuity and responsibility for third parties that can access data or systems.
A partner should be able to show evidence of control operation, not only a policy document. That includes access reviews, penetration-test remediation, incident drills, alert handling records and reconciliation results.
What evidence and response workflows should be ready before a cyber-fraud claim
A claim and an investigation usually depend on a coherent record. Preserve evidence before making broad system changes, but isolate compromised credentials, accounts or endpoints when necessary to prevent further loss. Use a documented chain of custody and record who collected each item, when and from which system.
The evidence pack should normally include:
- the incident timeline and initial detection source;
- loan application, KYC, underwriting, approval and override records;
- beneficiary and contact-change history;
- payment files, bank responses, reconciliation records and return messages;
- identity, access, API gateway, application, database, endpoint and network logs;
- privileged-access and service-account activity;
- relevant emails, messages, call records and customer confirmations, collected lawfully;
- partner notifications, contractual obligations and control attestations;
- forensic reports, root-cause analysis and remediation decisions; and
- notifications to insurers, banks, law enforcement, RBI, CERT-In and other relevant authorities.
CERT-In's Directions under section 70B of the Information Technology Act require covered entities to enable ICT-system logs and maintain them securely for a rolling period of 180 days. They also require a designated point of contact and cooperation with CERT-In directions. The applicable reporting and preservation duties should be assessed with legal and compliance teams for the specific event.
As of November 19, 2026, the RBI's NBFC cybersecurity directions state that cyber incidents are to be reported on the RBI's DAKSH platform within six hours of detection, and that NBFCs should proactively notify CERT-In. Teams should confirm the applicable direction, entity classification and reporting route before acting on a live incident.
The operational workflow should have one incident lead, one evidence owner, one regulatory and legal lead, one insurer or broker contact, and one communications owner. Use the claims layer for incident reporting and tracking to structure intake, documents, status updates, task ownership and partner hand-offs where that fits the operating model.
How to design cyber and fraud protection for an embedded lending product
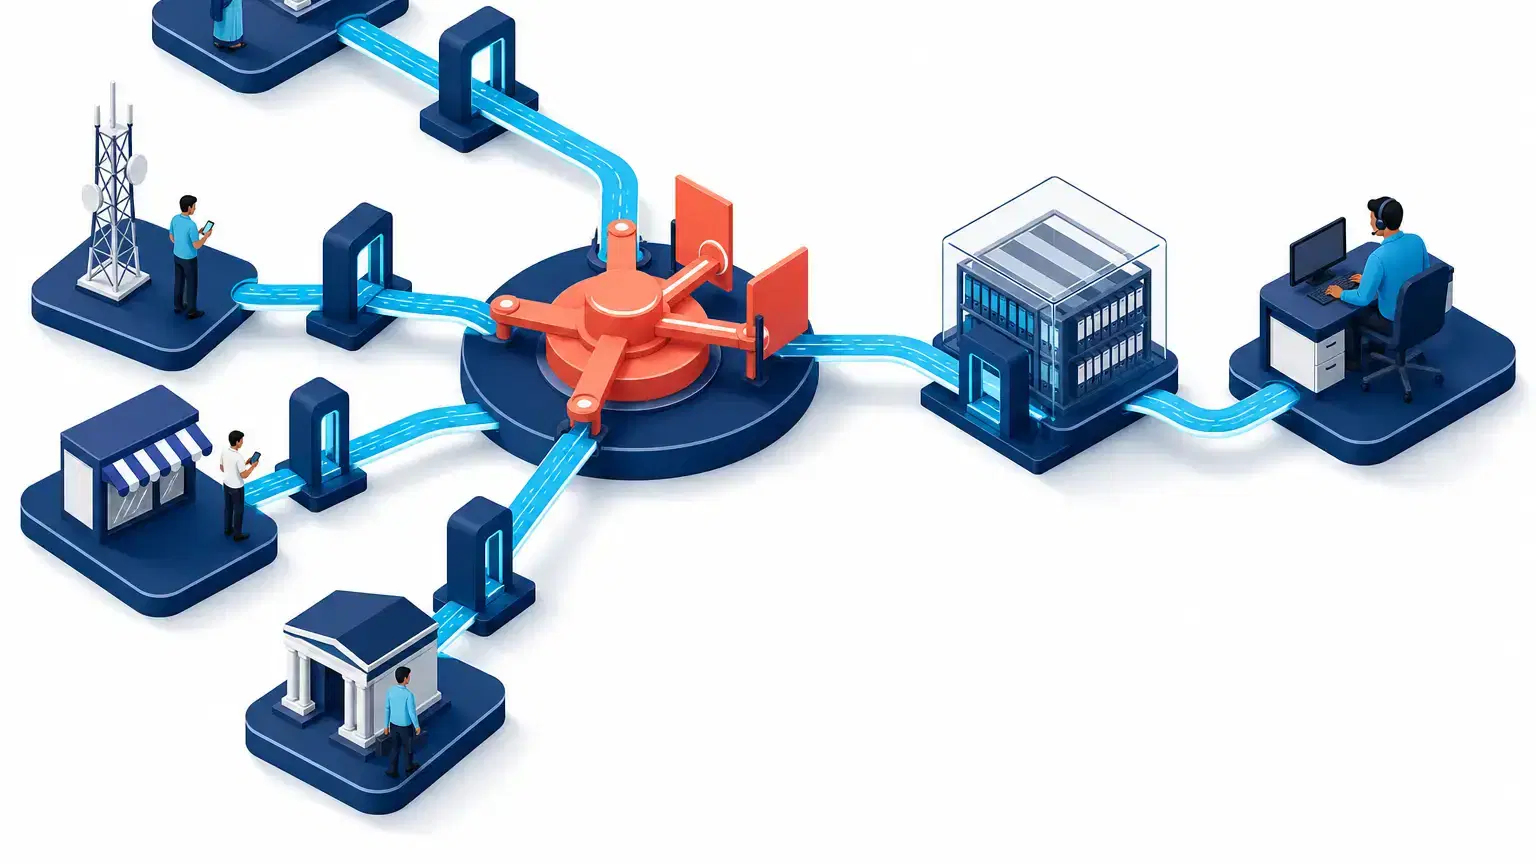
Embedded lending creates several customer and technology hand-offs. The lender may own the credit decision and funds, while a platform owns the interface, customer relationship, data collection or workflow orchestration. Protection should be designed around those hand-offs rather than added as a generic policy after launch.
A practical design has six layers:
- Risk mapping: identify every system, role, vendor and data flow from customer acquisition to repayment.
- Control ownership: document who validates identity, beneficiary details, device risk, payment instructions and exceptions.
- Event-based cover: decide whether the use case needs cyber, crime, funds-transfer, social-engineering, liability or another protection structure.
- Customer and partner disclosures: explain the relevant protection, exclusions, claims route and responsibilities in clear language.
- API and servicing integration: trigger enrolment, record policy or cover status, expose required servicing events and route claims evidence through controlled interfaces.
- Testing and governance: run fraud scenarios, review access, reconcile payments, measure alert outcomes and update the risk assessment after incidents.
For platforms serving multiple financial partners, the partner integration model for platform businesses illustrates the importance of designing distribution and servicing around the platform workflow. For API-led insurance operations, API infrastructure for embedded insurance workflows can support discussions about integration, product configuration and servicing hand-offs.
A lender should also decide whether the policyholder is the NBFC, platform, partner or another entity, and who is eligible for benefits. Those choices affect data access, notification duties, customer communication, claims evidence and the commercial arrangement. The final structure should be reviewed by the relevant insurance, legal, compliance and regulatory teams.
FAQ: Does cyber insurance replace fraud controls for an NBFC?
Does cyber insurance replace fraud controls for an NBFC?
No. It transfers a defined portion of financial risk. It does not replace access controls, approval segregation, beneficiary validation, transaction monitoring, incident response, regulatory reporting or partner oversight. Weak controls can increase loss, delay detection and create issues under policy conditions.
Can a cyber policy respond when an employee or partner changes a beneficiary?
It may, depending on the policy's definition of a covered event, the person's status, the type of instruction, applicable exclusions and whether required safeguards were followed. Do not assume that an internal action, authorised payment or partner error is covered merely because technology was involved.
Should the lender buy cyber cover or crime cover?
That is a risk-transfer decision based on the loss scenarios, policy wording, balance-sheet exposure, contractual allocation and available limits. Many loan-diversion scenarios can involve both cyber compromise and fraudulent funds movement, so the lender should compare the relevant insuring agreements rather than selecting a product by label alone.
What should partners agree before launching embedded lending?
Agree control ownership, access standards, beneficiary-change rules, log retention, alert escalation, incident notification timeframes, customer communication, recovery support, audit rights, evidence access and insurance responsibilities. Put those duties into the operating agreement and test them before a live incident.
A practical 30-day readiness checklist for lenders and partners
Days 1 to 7: establish the facts and exposure
- Map the approval-to-disbursal workflow.
- List every system and partner that can alter critical fields.
- Review recent beneficiary, contact and payment changes.
- Identify privileged users, service accounts and API credentials.
- Confirm log availability, retention and time synchronisation.
- Create a single incident and evidence register.
Days 8 to 15: test preventive and detective controls
- Run a sample review of approved loans and released payments.
- Test maker-checker controls and exception approvals.
- Challenge bank-account and beneficiary validation.
- Review alerts for unusual device, user, API and payment behaviour.
- Remove dormant access and rotate exposed secrets.
- Confirm partner escalation contacts and response obligations.
Days 16 to 23: prepare response and insurance evidence
- Build an incident playbook for suspected diversion.
- Assign legal, regulatory, forensic, communications and insurer contacts.
- Prepare evidence-collection and chain-of-custody templates.
- Check policy notification requirements, deductibles, sub-limits and exclusions.
- Conduct a tabletop exercise with the NBFC, LSP, platform and key bank partners.
- Confirm the route for customer complaints, payment recalls and recovery actions.
Days 24 to 30: close gaps and govern the programme
- Document control weaknesses and remediation owners.
- Present material findings to the appropriate management or board committee.
- Update partner contracts, service-level terms and audit rights.
- Record the risk-transfer decision and the scenarios that remain uninsured.
- Set recurring reviews for access, beneficiary changes, alerts, reconciliations and incident drills.
- Publish only confirmed incident facts, with legal and regulatory review before external communication.
Loan diversion prevention is strongest when credit, payments, cybersecurity, fraud, partnerships and insurance teams work from the same event model. NBFC cyber fraud insurance can form part of that programme, but the value of the cover depends on the quality of the controls, records and response around it.
Lenders and embedded-finance partners can Book a demo with BharatSure to explore a white-label cyber or fraud protection journey, with API integration, servicing and claims tracking designed around their loan or customer workflow. Cover, exclusions and claim decisions depend on the policy terms.
Frequently asked questions
Does cyber insurance replace fraud controls for an NBFC?
No. Insurance is a financial-risk transfer tool, not a substitute for approval controls, segregation of duties, access security, transaction monitoring, incident response or regulatory reporting. A policy may also contain exclusions, deductibles, sub-limits, warranties and conditions that affect a claim.
Can cyber insurance cover diverted loan proceeds?
Possibly, but not automatically. The answer depends on whether the loss falls within the insured cyber, crime, social-engineering, funds-transfer or other insuring agreement, and whether exclusions and policy conditions apply. The policyholder should map the event to the exact wording with its broker, insurer and legal advisers.
What should an NBFC preserve after suspected loan diversion?
Preserve approval records, KYC and borrower communications, beneficiary-change history, API and database logs, authentication events, privileged-access activity, device and network evidence, payment instructions, alerts, call recordings where lawful, investigation notes and correspondence with banks, partners, law enforcement, regulators and insurers.
Sources
- RBI Digital Lending Directions, 2025 — rbi.org.in
- RBI's NBFC cybersecurity directions — rbi.org.in
- Directions under section 70B of the Information Technology Act — cert-in.org.in
- BharatSure cyber insurance product page — bharatsure.com
- Partner integration model for platform businesses — bharatsure.com
- Claims layer for incident reporting and tracking — bharatsure.com
- API infrastructure for embedded insurance workflows — bharatsure.com
- Book a demo with BharatSure — bharatsure.com